Podcast
Descrição do episódio:
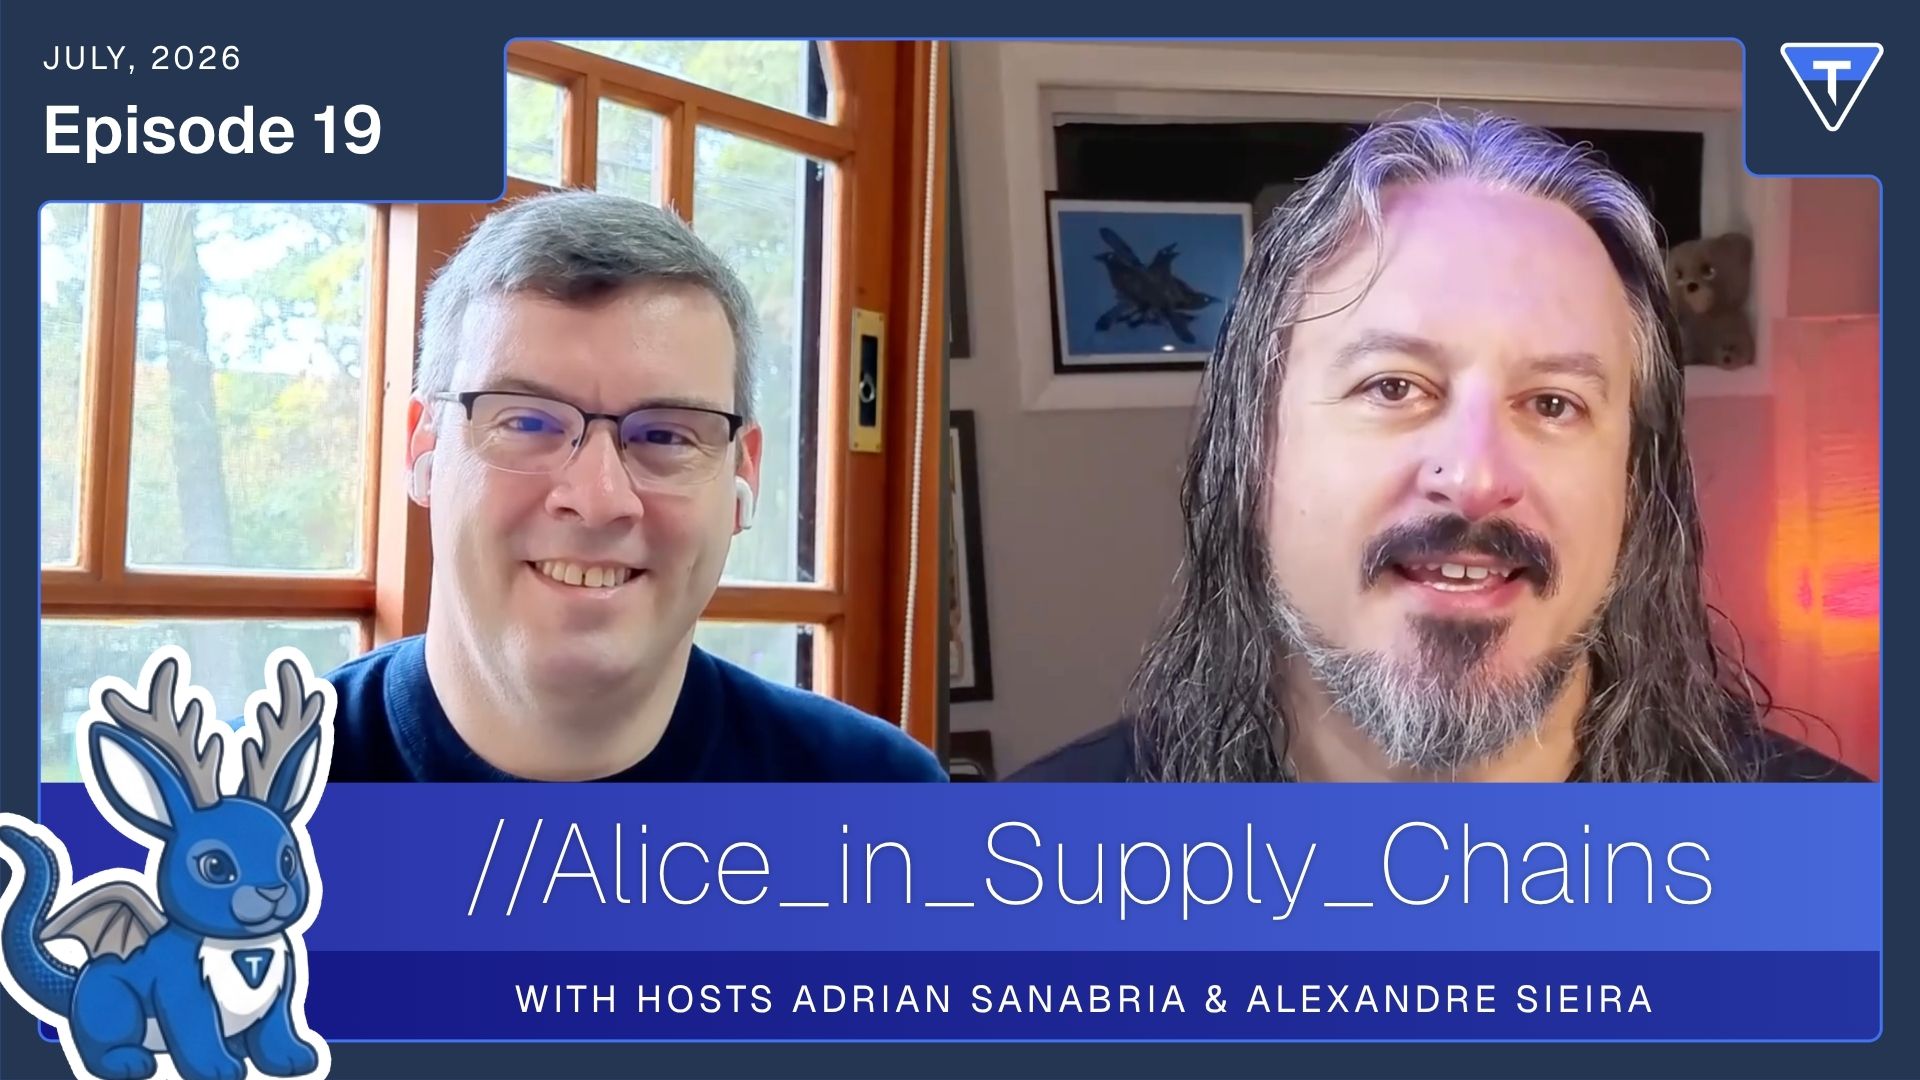
Episode 19 of Alice in Supply Chains explores how cyber risk is evolving beyond traditional security concerns and why organizations need to rethink how they measure, manage, and communicate risk. Adrian Sanabria and Alexandre Sieira discuss the latest developments influencing the cybersecurity landscape, from the real financial impact of breaches and emerging software supply chain threats to practical approaches for third-party cyber risk management and the evolving regulatory environment. Whether you're responsible for security, risk, procurement, or compliance, this episode offers valuable insights into the challenges shaping cyber risk management today.

Notas do episódio:
Here, Alexandre and Adrian dig into Verizon's first-ever Breach Impact Study, a companion to the DBIR built on roughly 70,000 cyber insurance claims (accepted and rejected) contributed via Cyber AcuView between 2019 and late 2025. The medians-only approach (no averages allowed!) makes this one of the most honest looks at breach costs yet, and the findings vindicate a recurring theme of the show: availability, not confidentiality, drives losses. Business interruption has the highest median claim (~$90K) and grew 51% year over year, while regulatory fines turn out to be the smallest loss category — so maybe stop leaning on "the regulator will fine us" to justify security budgets.
Software supply chain incidents are just 2% of claims but punch far above their weight, with immediate impacts more than double the rest of the dataset and extreme losses topping $100 million — cases that overwhelmingly hit policy caps, meaning the true economic damage is even higher. Adrian connects this to the rise of cascading breaches (Trivy → LiteLLM → everyone downstream), and the pair discuss why this kind of concentrated, systemic risk terrifies insurers and may reshape coverage terms.
Story two is Gartner's new "Mastering TPCRM" document series, which Adrian and Alexandre praise as unusually prescriptive and genuinely useful: frameworks for roles and responsibilities across security, legal, procurement, and — critically — business owners, plus a starter TPCRM policy you can adapt. Alexandre argues the make-or-break factor for any TPCRM program is whether business owners formally own the risks they accept, rather than treating the process as a checkbox that must not slow down contracting.
Finally, Schrems III is nigh: with the US Supreme Court's ruling undermining the independence of agencies like the FTC — the very foundation of the EU-US Data Privacy Framework — Max Schrems is poised to strike down transatlantic data transfer agreement number three. Alexandre walks through why the EU has painted itself into a corner (idealistic legislation, total dependence on US cloud, AI, and OS providers), what the $307 billion per year in EU spending on US cloud services means for both sides, and why every company with a transatlantic footprint should be talking to their legal counsel now.Links:
- Tenchi Conference 2026: Details, tickets, and CFP - https://luma.com/vvzsmej9
- Story 1: Verizon Breach Impact Study - https://verizon.com/dbir
- Story 2: Gartner’s Series on Mastering TPCRM - https://www.gartner.com/en/documents/7907309
- Story 3: Schrems III is Nigh - https://kaynemcgladrey.com/blog/when-the-load-bearing-wall-comes-down/
Show Transcript
Assista ou ouça os episódios completos em Inglês
Episódios Recentes
Episode 21
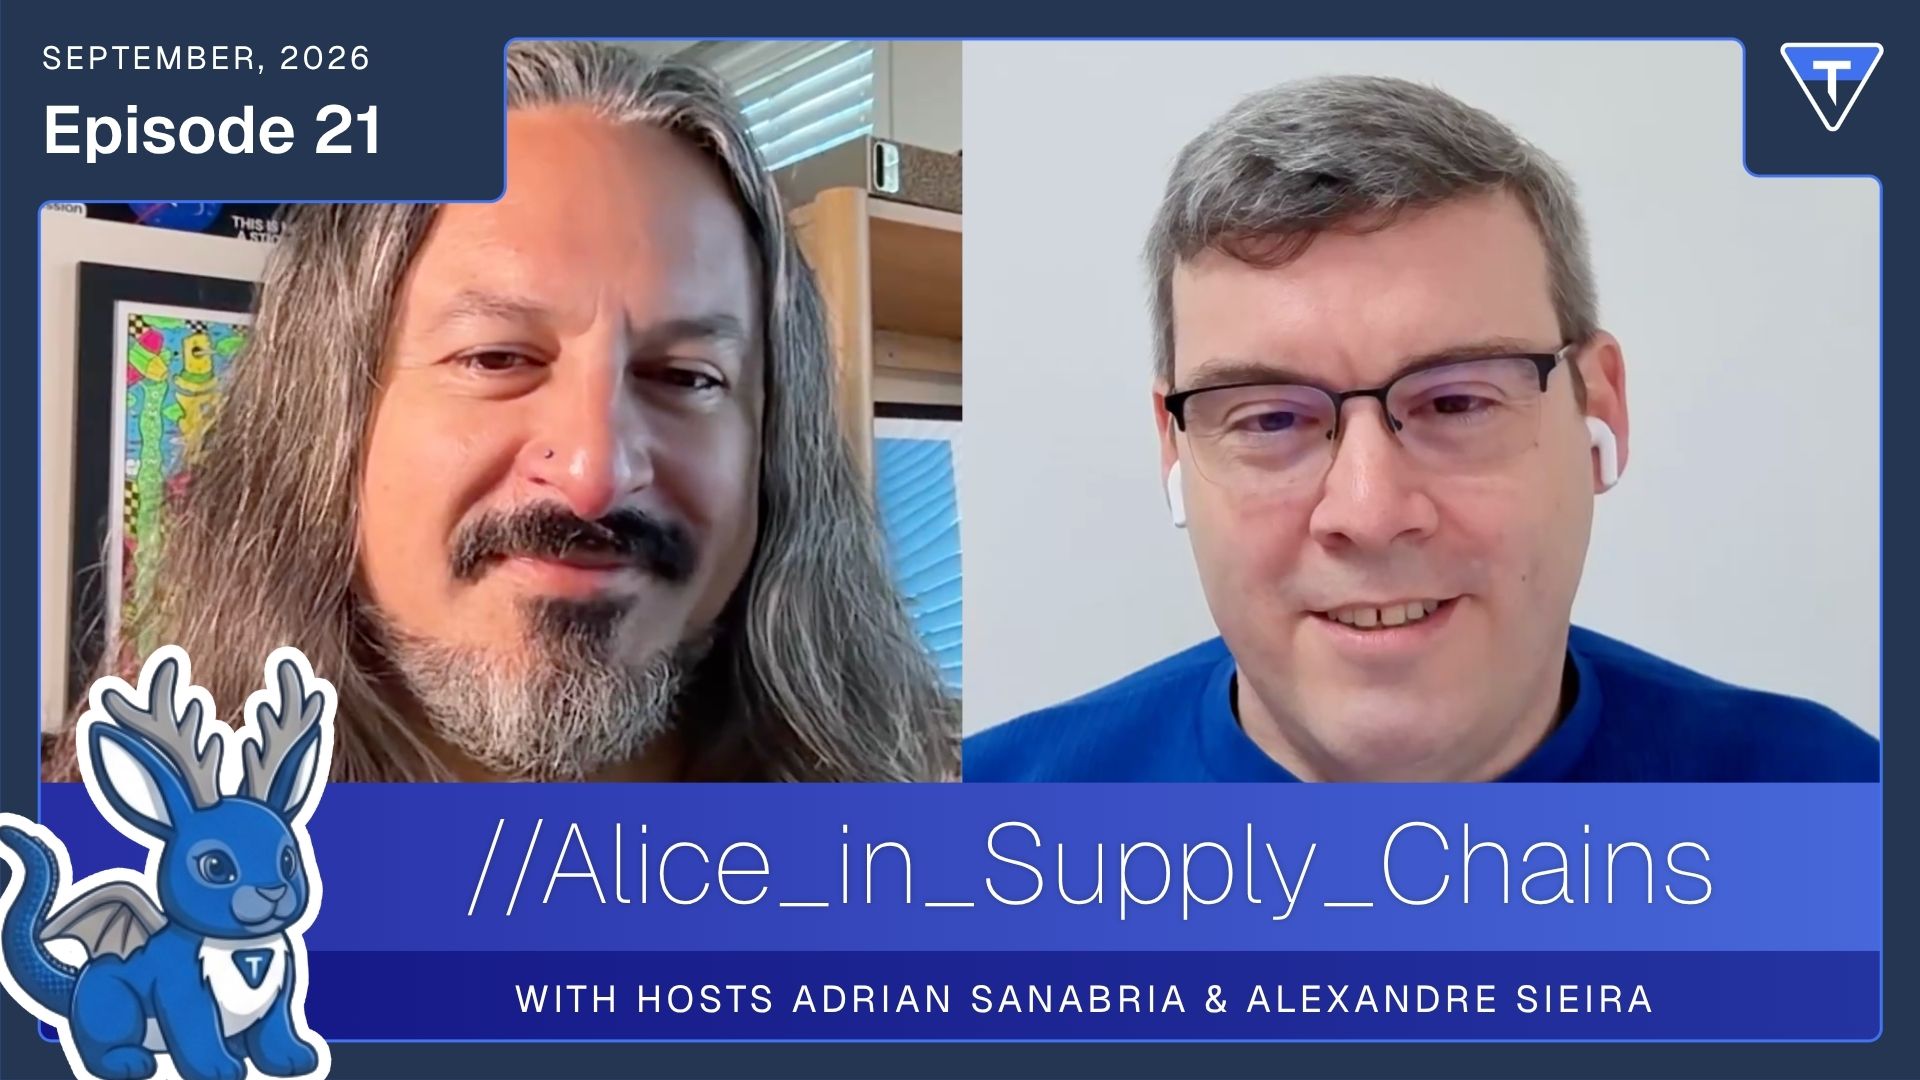
In this episode of the Alice in Supply Chains Podcast, Adrian Sanabria and Alexandre Sieira discuss four stories shaping third-party cyber risk management - from a BGP hijacking that compromised software updates to emerging AI risks, the rise of inside-out scanning in financial institutions, and proposed UK restrictions on risky technology suppliers.
Episode 20 | Recorded Live at Black Hat in Las Vegas!
On episode 20, Adrian and Alexandre discuss four recent stories shaping third-party and AI risk: SOC 2 commitments deferred by vendors, the lessons from Brazil’s PSTI security requirements, AI agents and security incidents involving Hugging Face, OpenAI and Anthropic, and a prompt injection case involving outside counsel in Brazil. The episode explores what these incidents mean for TPCRM, vendor assurance, regulatory compliance, AI governance, and third-party contracts.
Episode 18
In this month's episode of Alice in Supply Chains, Alexandre Sieira and Adrian Sanabria cut through the AI-hacking hype to focus on the vulnerabilities that are actually driving ransomware and cyber insurance claims: old, unpatched systems and forgotten assets. They also examine the growing dispute between Microsoft and security researchers, npm's new package provenance features as a partial defense against supply chain attacks, and the broader European push for digital sovereignty.