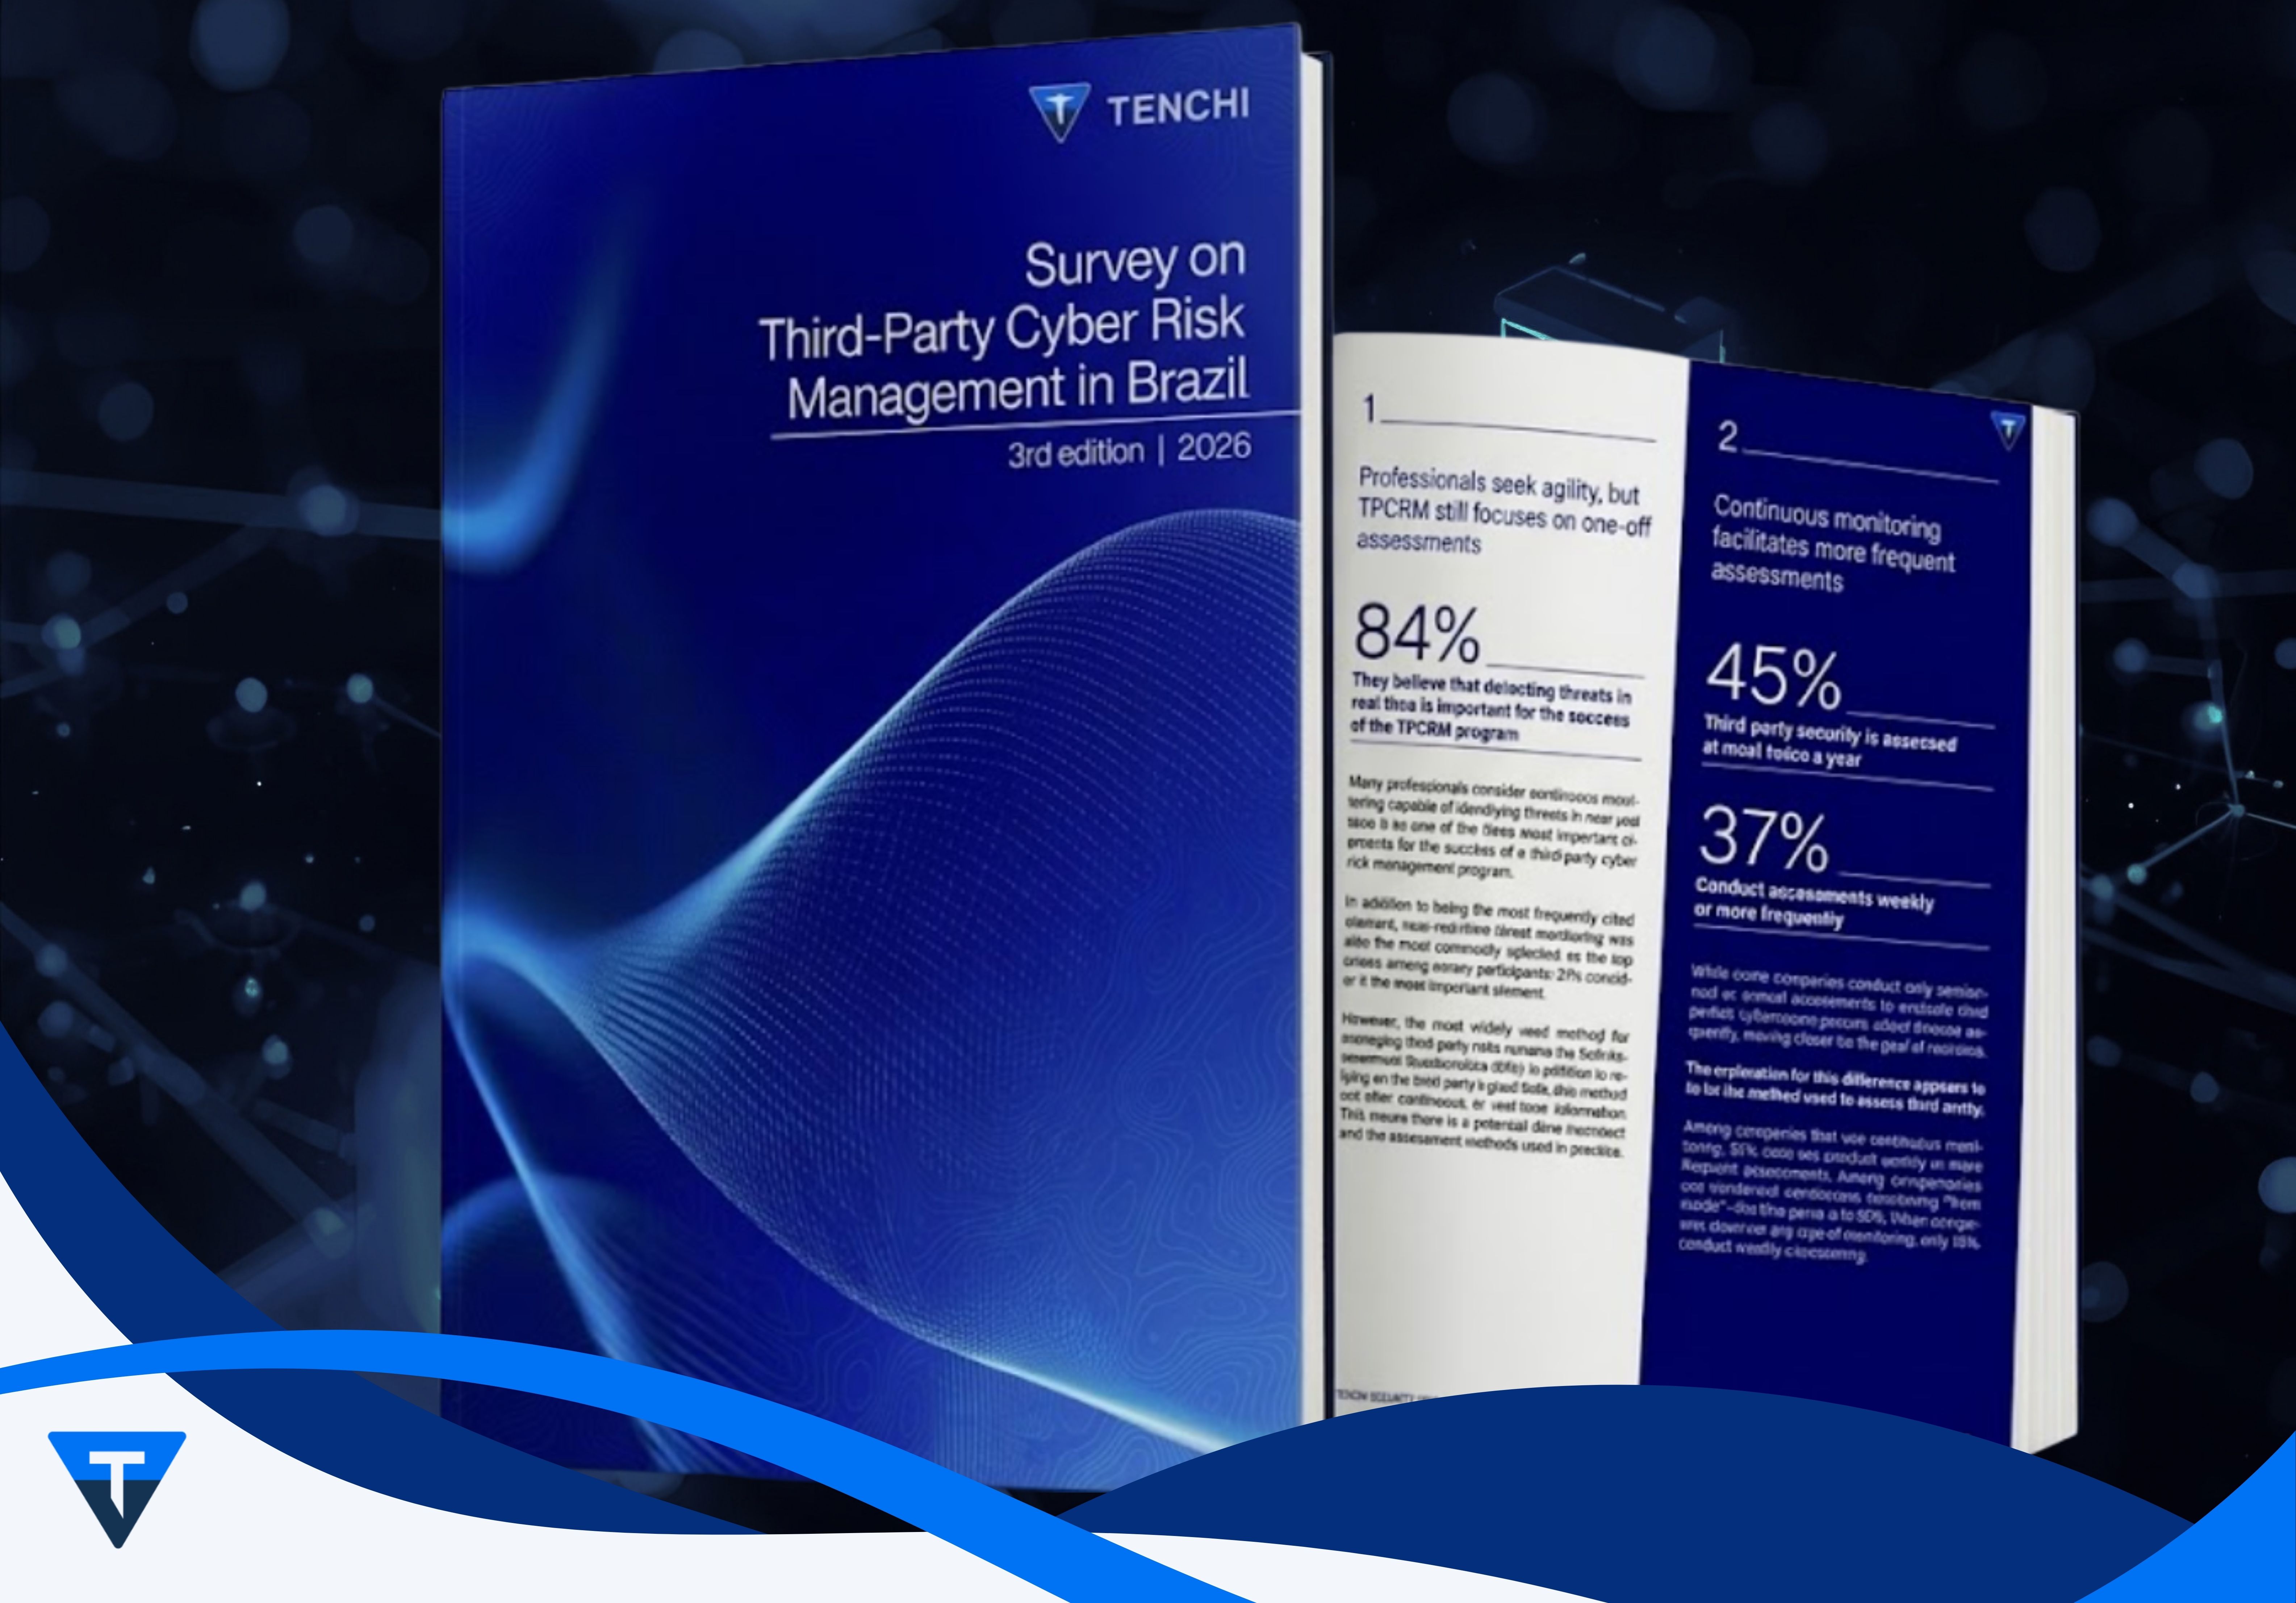
For the third year in a row, Tenchi Security surveyed professionals in information security, risk management, privacy and procurement to understand how Brazilian companies handle cyber risk from their suppliers and partners. The 2026 edition brings together respondents from sectors such as financial services, insurance, telecommunications, healthcare and retail.
Now in its third edition, this exclusive report by Tenchi Security provides an updated overview of TPCRM methodologies, gaps, and opportunities.
84% of professionals say continuous monitoring is the most important element for a successful TPCRM program. In practice, the most widely used method is still the Self-Assessment Questionnaire, adopted by 76% of companies with a structured program.
What you'll find in the report:
- Why point-in-time methods, such as questionnaires and certifications, still dominate even though professionals place little trust in them
- The cloud blind spot: 84% rank cloud among their top concerns, yet 52% have no visibility into their third parties' cloud
- How assessment frequency changes with continuous monitoring: 53% of companies that use it assess their third parties every week
- How TPCRM programs have evolved since 2023, including third-party coverage and the training companies offer them
- The third-party incidents that defined 2025 and 202, and more
Download the full study by filling out the form below: